
F5 Setting up Advanced WAF Corporate Training
Set up F5 Advanced WAF end to end: policies, attack mitigation, bot defense, and logging in guided labs.
Your team learns to protect web applications with F5 Advanced WAF. Employees build security policies, block OWASP-style attacks, defeat bots, and wire up logging in guided labs led by practitioners. Each session is tuned to your F5 versions, applications, and workflows.
Instructor-led group trainingVirtual / on-site / hybrid10+ languagesDelivered in English, Spanish, Mandarin, German, Arabic, Portuguese, Hindi, French, Japanese, Italian, and more100+ countriesWe have delivered in United States, United Kingdom, India, Canada, Germany, France, Netherlands, UAE, Saudi Arabia, Singapore, Australia, Japan, Brazil, South Africa and 90+ more countries
How we build an application-shielding security team
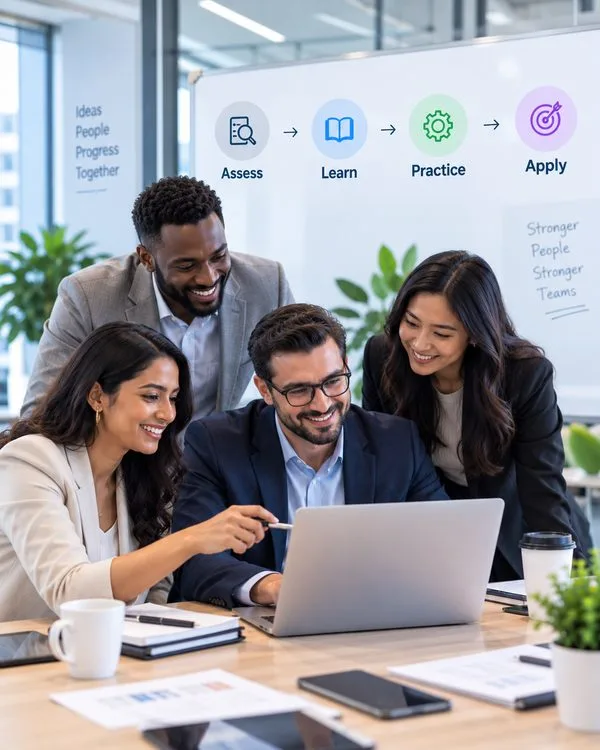
EDSTELLAR CYBERSECURITY CAPABILITY MODEL
Assess WAF maturity
Skill checks map your team's web security and policy baseline.
Set shared policy standards
One shared standard for policy design, tuning, and rollout.
Practice in guided labs
Labs cover policies, attack mitigation, and bot defense.
Measure the lift
Lab reviews benchmark each engineer's WAF administration capability.
Scale across teams
One standard rolls out across applications, regions, and estates.

Need more than one program?Get a group quote
Trusted as a Leading Corporate Training Provider by




Program Overview: What is F5 Setting up Advanced WAF?
F5 Setting up Advanced WAF is a 24-hour, hands-on program for security engineers and application teams who need web applications defended, not just delivered. It covers WAF concepts on the BIG-IP platform, security policy fundamentals, OWASP-style attack mitigation, bot defense, behavioral controls, and logging and event correlation. Participants build policies against live attack traffic in the lab.
The labs are adversarial by design. Participants tune security policies while simulated attacks probe for gaps, configure bot defenses against automated abuse, and learn to read the event logs that separate false positives from real breaches. Instructors with WAF deployment experience review every policy, showing where over-blocking breaks the business and under-blocking invites it. The difficulty ramps from signature basics to behavioral analysis, and the program ends with a capstone where each team hardens and defends a production-ready WAF deployment.
A misconfigured WAF is either a wall nobody can pass, including customers, or a decoration attackers walk around. This program teaches the tuning discipline that makes a WAF effective: understand the application, baseline its behavior, then enforce. Teams learn to balance protection with usability and to prove the policy works before it meets real traffic.
The capstone puts the team's WAF under fire: a production-ready deployment, with policies, bot defenses, and logging the team configured, subjected to a structured attack exercise. Reviewers score both the blocks and the false positives, because a WAF that stops the business is a failure too. Engineers walk out with a deployment pattern they trust and the tuning judgment to keep it sharp as applications evolve.
Six modules and 24 hours: WAF concepts, policy fundamentals, attack mitigation, bot defense and behavioral controls, and logging and reporting. Every module pairs concepts with a guided lab, so each technique is practiced. It closes with a capstone production deployment the team builds, tunes, and defends in review.
Delivery is hybrid across virtual and onsite sessions, scheduled around your calendar. Cohorts train as one group or split into batches, with session materials and lab guides included for every participant.
What's Included in this Workshop for Your Enterprise Teams
- 1
Policy building labs
Create transparent and blocking policies for sample apps.
- 2
Attack mitigation exercises
Block scripted attacks and tune false positives.
- 3
Bot defense workshops
Stop credential stuffing while sparing good automation.
- 4
Logging and rollout labs
Wire telemetry to SIEM and stage policies to blocking.
- Instructor-led delivery across virtual, onsite, and hybrid
- Guided labs in every module with instructor coaching
- Capstone WAF deployment, reviewed with your team
- Flexible scheduling around your calendar
- Lab guides and reusable policy templates included
- Group size and batches set along with you
Build your team's skills. Anywhere in the world.
Real-world use cases
from day one
Instructor-led training
for your teams
Delivered globally
in 100+ countries
Enterprise Training Solutions Customized for Your Company
One partner for instructor-led corporate training, delivered the way your teams work.
Request a Training Quote- Customized Training Delivery
- Scale Your Training: Small to Large Teams
- In-person Onsite, Live Virtual or Hybrid Training Modes
- Plan from 2000+ Industry-ready Training Programs
- Guided Technical Labs, Led by Industry Experts
F5 Setting up Advanced WAF Course Topics and Program Outline
A tailored 24-hour, six-module workshop: one learning journey from WAF concepts to a capstone production deployment. Sessions pair concepts with labs on real-world use cases. Materials include lab guides, policy templates, and tuning checklists for every participant.
Built by Edstellar with application security practitioners
Built by practitioners who run F5 WAF estates in production, shaped around your stack and use cases.
Skill checks baseline your team's web security, WAF, and F5 platform familiarity before training begins.
Live instruction covers WAF concepts, policy fundamentals, and enforcement modes across 6.5 focused hours.
Guided labs build attack mitigation, bot defense, and logging skill across 12.5 hours of supervised practice.
Your team ships a production-ready WAF deployment in a 5-hour capstone, reviewed against operational standards.
From WAF concepts to a capstone production deployment, every technique is practiced in guided labs.
Delivered as
Delivered as a hybrid program of live instruction and guided labs, scheduled around your team's calendar in flexible batches.
Tour the BIG-IP management interface in the guided demo environment and map each WAF capability to your team's application security workflows.
learnThe WAF role in application defense
BIG-IP modules and management interfaces
Common web attack classes
Lab access and topology orientation
Create a transparent security policy for a sample application, review learning suggestions, and accept the entities that belong in the policy.
learnTransparent versus blocking enforcement
Security policies and policy templates
URLs, parameters, and entity management
Learning suggestions and policy tuning basics
Launch scripted SQL injection and XSS attacks against the lab application, confirm the WAF blocks them, then tune two false positives out of the policy.
practiceAttack signatures and signature sets
SQL injection and XSS mitigation
False positive analysis and tuning
Staging: moving entities to blocking
Enable bot defense on the lab application, simulate a credential stuffing run, and confirm it is blocked while approved monitoring scripts keep working.
practiceBot signatures and behavioral detection
CSRF protection for application flows
Brute force and credential stuffing controls
Allowlists for legitimate automation
Forward WAF events to the lab SIEM, build an operations report on blocked attacks, and trace one incident from alert to root request.
practiceLocal and remote logging profiles
Working the ASM event log views
Reports for operations and audits
SIEM forwarding and event correlation
Deploy the production-ready WAF policy end to end, then present the rollout plan and defend every enforcement decision in the instructor review.
applyFull policy build for the target application
Staging-to-blocking rollout plan
Runbook and handoff documentation
Design defense and peer review
Customize This Program Tailored to Your Team?
Tell us your training needs: what your team already works with, the level they’re at, and the topics you want them to focus on. We’ll adjust the modules, duration and hands-on labs, and send you a customized outline for your group.
Key Skills and Outcomes Your Team Will Gain
Seven job-ready outcomes your team will demonstrate by the end of the program. Each competency is practiced in guided labs and reviewed in the capstone deployment.
Explain how a WAF protects applications
Describe where Advanced WAF sits in the defense stack and which attack classes it mitigates.
Build WAF security policies
Create transparent and blocking policies with disciplined entities and learning-driven tuning.
Mitigate OWASP-style attacks
Enable signatures to block SQL injection, XSS, and related attacks while controlling false positives.
Defeat bots and session abuse
Configure bot defense, CSRF, and brute force protections that spare legitimate automation.
Operate WAF logging and reporting
Build logging profiles, work event views, and forward telemetry to a SIEM for correlation.
Roll out policies safely
Move policies from staging to blocking with testing, rollback points, and runbook documentation.
Deliver a reviewed WAF deployment
Ship a production-ready WAF policy and defend every enforcement decision in the capstone review.
Teams that Benefit from this F5 Setting up Advanced WAF Group Training
This group training is built for teams that protect web applications and want WAF enforcement that blocks attacks without breaking releases. Content adapts to each cohort's roles, F5 versions, and experience, so every batch practices the workflows it owns, from policy building to incident tracing.
Ship applications with WAF protection baked in.
AppSec engineers learn to design WAF policies, mitigate OWASP-style attacks, and tune enforcement without breaking releases.
Workflow friction
- Unprotected public endpoints
- Noisy blocking policies
- Slow tuning cycles
How the program helps
- Blocking-mode WAF policies
- Fewer exploitable app flaws
- Tuned, low-noise enforcement
Practice use cases
- Policy design labs
- Attack mitigation
- False positive tuning
Read WAF telemetry like an investigator.
Analysts learn to work WAF event logs, correlate blocked attacks with SIEM data, and escalate with evidence.
Workflow friction
- WAF alerts without context
- Missed application attacks
- Weak escalation evidence
How the program helps
- Faster attack confirmation
- Correlated WAF and SIEM views
- Evidence-rich escalations
Practice use cases
- Event log analysis
- SIEM correlation
- Incident writeups
Operate WAF as reliable infrastructure.
Platform teams practice deployment patterns, logging pipelines, and upgrade-safe policy management for WAF estates.
Workflow friction
- Snowflake WAF configs
- Lost telemetry on incidents
- Risky policy pushes
How the program helps
- Repeatable WAF deployments
- Reliable log pipelines
- Safe policy change process
Practice use cases
- Deployment labs
- Logging setup
- Change drills
Extend perimeter defense to the app layer.
Network security staff learn where WAF fits beside firewalls and ADCs, and how to hand off cleanly between layers.
Workflow friction
- Gaps between network and app layers
- Overlapping, conflicting controls
- Unclear ownership
How the program helps
- Layered defense coverage
- Clean firewall-to-WAF handoffs
- Consistent enforcement story
Practice use cases
- Architecture mapping
- Handoff playbooks
- Coverage reviews
Cohorts train as a cross-functional workforce, with each small group aligned on shared policy and tuning standards.
Prerequisites: This program benefits application security engineers, WAF administrators, and DevSecOps staff who protect web applications or plan to. Basic HTTP and web concepts help but are not required: the opening module establishes WAF fundamentals before any policy is built, and every lab adapts to each cohort's F5 versions and experience.
WAF administrator to application security engineer
Move from WAF fundamentals to advanced enforcement: each level adds hands-on depth, from describing enforcement modes to owning tuned, production-ready WAF estates.
A program that grows with security careers, from first WAF policy to confident production deployment ownership.
Different Teams, Locations, Time Zones, or Languages? We've Got You Covered.
Whether your teams are spread across countries, time zones, languages, or experience levels, we deliver tailored training programs that ensure a consistent learning experience across your global workforce.
Certificate of Training Completion.
On successful completion, employees receive an Edstellar course completion certificate, recognizing their commitment to ongoing learning and professional development. It validates the skills they have built and motivates them to keep growing and contribute to organizational success.
Earned, not attended. Awarded on completion of all hands-on labs and the capstone project.
Training Delivery Modes: Onsite, Virtual and Hybrid
Live instruction with guided labs in every module, available across onsite, virtual, and hybrid formats to fit your team's schedule.
Onsite Training
Instructor-led training at your offices, with lab scenarios adapted to mirror your applications. The instructor works alongside the team in person, reviews policies together, and tunes exercises to your F5 estate and workflows.
- Instructor-led training at your offices
- Lab scenarios mirroring your applications
- In-person coaching and reviews
- Exercises tuned to your F5 estate and workflows
Live Virtual Training
Live virtual sessions on Zoom or Teams with screen-shared policy walkthroughs, breakout labs, and real-time reviews. Your team gets the same guided labs and instructor coaching as onsite, from anywhere.
- Live virtual sessions on Zoom or Teams
- Screen-shared walkthroughs and breakout labs
- Real-time review with the instructor
- Same guided labs as onsite, from anywhere
Hybrid Training
Instructor-led sessions mix onsite and virtual delivery with guided labs throughout. Teams practice WAF policy building, attack mitigation, and tuning while the instructor coaches and reviews work. Hybrid keeps scheduling flexible without losing live interaction.
- Live instruction across onsite and virtual sessions
- Guided labs with instructor coaching and reviews
- Real application security workflows with hands-on practice
- Flexible scheduling without losing live interaction
Need a Customized Training Format That Works for Your Team?
Our training delivery is customized to your team's schedule, full days, half days, sessions spread across weeks, or modular formats. Share your preferred timeline, and we'll plan the training around it.
Frequently Asked Questions
Share your team size, timelines, and delivery preference, and we will send a detailed per-group quote with batch options.
Yes. Book a discovery call and we will map your application estate, WAF maturity, and goals to a tailored training plan before you commit.
Yes. Live virtual sessions run on Zoom or Teams with the same guided BIG-IP labs and instructor coaching as onsite delivery.
Yes. The instructor runs the full program at your offices, with lab scenarios adapted to mirror your applications and traffic patterns.
The program runs 24 hours of instructor-led training, usually across three to six days or weekly sessions on a flexible, mutually agreed schedule.
Question Not Answered Here?
Put it in the request. A training specialist answers it directly, within one business day.
Where this Training Fits in Your Team's learning path.
Setting up F5 Advanced WAF follows BIG-IP administration, because the WAF runs on that platform. With the WAF protecting web apps, your team extends protection to APIs and then tests the defences to confirm they stop real attacks.
ADMINISTER F5 BIG-IP
F5 BIG-IP Administration Training
Configure and manage F5 BIG-IP traffic, virtual servers and pools.
SET UP THE WAF
F5 Setting up Advanced WAF Training
Deploy and tune F5 Advanced WAF policies to protect web applications from common attacks.
SECURE APIS
API Security & Testing Training
Secure and test APIs, which WAF policies alone may not fully cover.
TEST THE DEFENCES
Vulnerability Assessment & Penetration Testing (VAPT) Training
Test your web apps and defences through vulnerability assessment and penetration testing.
Why Choose Edstellar as Your F5 Setting up Advanced WAF Corporate Training Provider
When comparing providers, Edstellar is the training partner teams choose for application security expertise and 5+ years of corporate training experience. Our methodology blends concise instruction with guided labs, and we share each trainer profile before booking. The result is measurable quality in the attacks your team blocks and the releases it keeps safe.
EXPERT TRAINERS
YEARS DELIVERING
ORGANIZATIONS TRAINED
CERTIFIED
Tailored
Every cohort's labs, policies, and attack scenarios are tuned to your applications and traffic patterns.
Proven Methodology
A learn, practice, apply arc moves your team from WAF concepts to a live production deployment capstone.
Practice-Based Learning
Guided labs in every module build policy design, attack mitigation, and tuning skill on realistic apps.
Expert Trainers
Practitioners who run F5 WAF estates in production lead every session.
Global Scale
One consistent program rolls out across application teams, regions, and delivery formats.
Measurable Outcomes
Lab checkpoints and the capstone review show exactly what your team can now protect and tune.
Tune F5 Advanced WAF Policies With Verified Protection and Useful Incident Evidence
Edstellar develops Advanced WAF capability through policy learning, attack mitigation, bot defense, and event correlation. Teams test protections against scripted traffic on a lab application while preserving legitimate behavior. The final deployment review examines enforcement decisions, false-positive handling, and incident traceability, with a rollout plan that reflects observed policy behavior rather than unchecked blocking.
- Step 01
Consult
We explore application-security responsibilities and HTTP familiarity, identifying gaps in WAF policy learning, false-positive analysis, bot controls, event correlation, and enforcement rollout decisions.
- Step 02
Plan
We establish BIG-IP WAF foundations before transparent policy learning, then attack mitigation and bot defense, followed by SIEM correlation and the reviewed deployment plan.
- Step 03
Align
We align F5 WAF expertise with application-security engineers, administrators, and DevSecOps teams, matching policy exercises to platform versions and establishing controlled attack-test boundaries.
- Step 04
Customize
We tailor sample application entities, scripted attacks, approved monitoring traffic, and incident logs to relevant web services, keeping all testing within the authorized lab application.
- Step 05
Execute
Participants tune policies, verify scripted attack blocking, and trace SIEM events, receiving feedback on false positives, legitimate bot access, and evidence supporting enforcement changes.
- Step 06
Evaluate
We assess the WAF deployment for demonstrated protection, preserved legitimate requests, traceable incident logs, and a rollout rationale that accounts for policy-learning and false-positive findings.
Also from Edstellar
Talent assessments
Psychometric, behavioral, leadership and 360-degree assessment.
→Training needs analysis
Needs analysis, gap identification, and a training roadmap.
→L&D consulting
Learning strategy, content, technology and ROI measurement.
→OD consulting
Org design, succession planning and cultural change.
→Managed training services
Training outsourcing, vendor management, logistics and administration.
→Coaching solutions
Executive and manager coaching that keeps skills in use.
Start an RFP shaped to your needs.
Answer three quick questions about team size, scope, and how often you need the program run, then send the request from the last step. Everything you choose travels with it, so you only fill this in once.
How many team members need training?
F5 Setting up Advanced WAF Training Packages & Pricing
Where L&D holds an annual budget, license packages price the whole year at once instead of raising a purchase order per workshop. Hours and licenses are pooled across teams, programs and locations, so unused capacity is not stranded in one department.
Starter
120
trainee licenses64 hours of group training
Tailored for SMBs
Growth
320
trainee licenses160 hours of group training
Ideal for growing SMBs
Enterprise
800
trainee licenses400 hours of group training
Designed for large corporations
Custom
Unlimited
trainee licensesDuration set by the rollout
Multi-region and multi-year
Training Packages & Pricing
Choose the training format that works for your team. Pricing is customized based on your requirements, cohort size, and delivery needs.
Request a Quote for F5 Setting up Advanced WAF Training for Your Team
Share your team size, F5 versions and application estate, and timelines to receive a tailored training plan and quote. Book a discovery call to discuss your goals; we confirm availability and respond with a proposal.